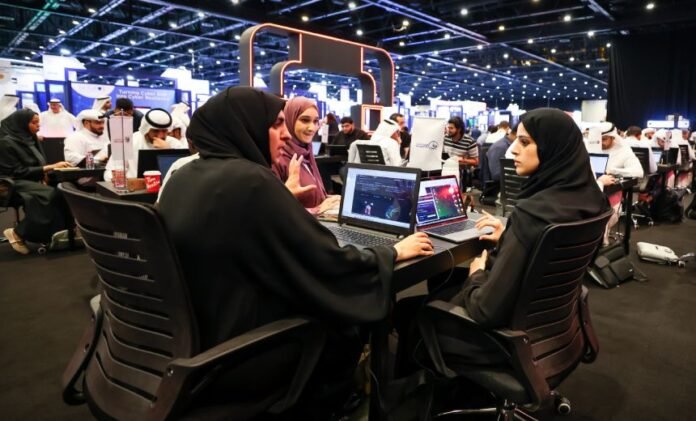
Hacking Contest Signals Growing Emphasis on Cyber Resilience in Government Organizations
Regulatory Development Summary
The recent capture-the-flag hacking contest held during the GISEC Global expo in Dubai illustrates a significant shift toward fostering a culture of proactive cybersecurity among government agencies. This initiative, spearheaded by local authorities, aims to sharpen the skills of cybersecurity personnel across various government sectors. While the contest itself was largely informational and competitive, it highlights a broader regulatory trend focused on enhancing cybersecurity measures among public sector organizations. Although specific regulations directly stemming from this event were not discussed, it reflects ongoing regional efforts to strengthen cyber resilience and may influence future regulatory frameworks, particularly under the auspices of the United Arab Emirates’ Cybersecurity Strategy.
Who Is Affected and How
Government entities in the UAE are the primary beneficiaries of this initiative, facing newly heightened expectations around cybersecurity competencies. This contest serves as a precursor to potential regulatory requirements that would impose stricter security protocols and continuous training for cybersecurity teams. Currently, entities operate under existing guidelines that emphasize basic compliance with cybersecurity best practices. However, the proactive competitive environment created by such contests signals a need for agencies to evolve their cybersecurity strategies beyond minimum compliance, embracing a more dynamic approach to risk management and response capabilities.
Key Compliance Requirements Breakdown
While the contest itself did not introduce formal requirements, it serves as a practical guide for government agencies looking to enhance their cybersecurity posture. Practitioners should focus on the following areas:
Vulnerability Assessment: Regular testing of systems through internal or external capture-the-flag events could become a de facto standard for ongoing vulnerability assessments.
Incident Response Simulation: Agencies should develop exercises similar to the contest to evaluate their incident response protocols, involving various departments to create comprehensive readiness plans.
Training and Development: Continuous professional development in cybersecurity skills is essential. This could align with frameworks like NIST CSF and ISO 27001, which emphasize employee training as part of a holistic security strategy.
Collaboration and Information Sharing: Establishing teams that can collaborate across government sectors will enhance information sharing protocols, a critical aspect of effective cybersecurity as outlined by frameworks such as MITRE ATT&CK.
- Performance Metrics: Agencies should develop and monitor specific performance metrics related to their cybersecurity capabilities, which could inform future resource allocations and policy development.
Penalties and Enforcement Landscape
As of now, there are no defined penalties or enforcement mechanisms directly tied to the hacking contest; however, as governmental bodies start to formalize regulations in response to these initiatives, organizations can anticipate stricter enforcement standards. Historically, a lack of compliance with evolving cybersecurity protocols has resulted in severe fines and reputational damage. Future misconduct in adhering to projected requirements may face similar outcomes. Regulatory bodies may look to global precedents to underpin these decisions as they draw lines in the sand concerning expectations.
Timeline and Implementation Considerations
While no specific deadlines have been set following the contest, organizations should prepare for increased regulatory scrutiny in the upcoming year. Implementation hurdles may include:
Resource Allocation: Agencies might face funding limitations that can impede substantial investments in cybersecurity training and infrastructure improvements.
Technical Complexity: Integrating advanced threat detection and response technologies will necessitate hiring and training personnel to operate these systems effectively.
- Third-Party Risk Management: As partnerships with technology firms become more common, establishing appropriate controls over third-party relationships will be essential.
Strategic Recommendations for Compliance Teams
To navigate this evolving landscape, compliance and cybersecurity teams should consider the following actionable steps:
Establish Cybersecurity Competitions: Organize in-house contests or collaborate with educational institutions to provide real-world training scenarios for personnel.
Develop Continuous Training Programs: Implement ongoing training initiatives that build on contest learnings, emphasizing hands-on, scenario-based learning.
Leverage Existing Frameworks: Map upcoming regulatory requirements against established standards like NIST CSF or ISO 27001 to streamline compliance efforts.
Documentation Practices: Maintain thorough incident documentation and training records to demonstrate compliance readiness during audits.
- Engage in Cross-Agency Collaborations: Form networks with other governmental bodies to share best practices and lessons learned from initiatives like the GISEC contest.
Full Circle Cyber Analyst Takeaway
The recent hacking contest at the GISEC Global expo represents a crucial inflection point for government cybersecurity, signaling a shift from compliance to proactive resilience. Agencies should not only prepare for impending regulations but also leverage this cultural change to enhance their cybersecurity competency. Prioritize investments in training and collaboration to ensure preparedness against evolving threats, which, in turn, will foster a robust security posture capable of tackling future challenges head-on.

