Phishing Platforms Evolve: New Threat Mimics Popular AI Tools
What Happened
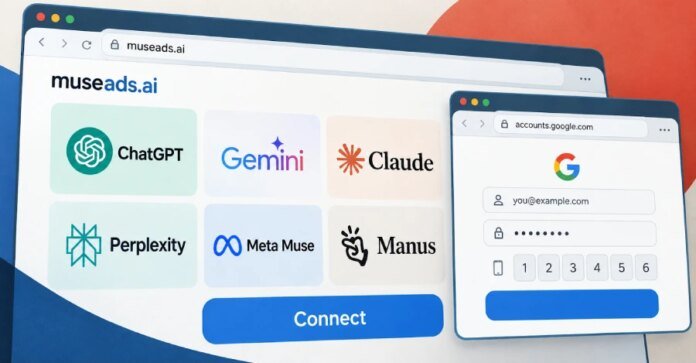
Recent cybersecurity research has unveiled a sophisticated phishing operation leveraging the popularity of artificial intelligence (AI) tools, specifically targeting platforms such as Google Gemini, Anthropic Claude, OpenAI ChatGPT, Perplexity, and Meta Muse. The scammers have developed a "human-operated phishing platform" that masquerades as legitimate advertising services promising campaign optimization and business-account connectivity. Initial reports indicate that unsuspecting users may be lured through deceptive communications with links to counterfeit applications designed to harvest sensitive information. This operation reflects a growing trend in cybercriminal tactics that utilize emerging technology to enhance their schemes. While exact metrics on the scale of the data compromised remain unclear, the implications could involve the exposure of significant personal and business data, exacerbating the risks for organizations across multiple sectors.
Why This Breach Matters
This incident signifies a notable evolution in phishing strategies, amplifying the use of AI narratives to deceive users. The obfuscation of identity through well-constructed imitations of reputable tools not only increases the potential for successful exploitation but also presents a concerning trend where phishing attempts follow technological advances. Unlike traditional phishing tactics, which largely relied on generic impersonation, this methodology tailors threats around high-demand tools and services, heightening the urgency for security teams to reassess their defenses. Comparatively, similar breaches have highlighted how agile attackers are in adopting trends; thus, organizations must be vigilant about the rapid evolution of attack vectors and be prepared for increasingly sophisticated threats that leverage widely-used technologies.
The Attack Chain: How It Likely Unfolded
Analysis of this phishing operation suggests it follows a multi-phase attack chain beginning with initial recruitment techniques on platforms where potential targets congregate—particularly business networks or social media. Attackers disguise their communications to appear as legitimate business offers or service enhancements, utilizing social engineering tactics to encourage interactions. Once a target engages, the scam most likely transitions to phishing sites designed to mimic authentic applications. During this phase, criminals often harvest credentials through forms resembling login prompts for popular AI tools, potentially leading to lateral movement within corporate networks if a victim’s access credentials are compromised. Such methods indicate a likely focus on dwell time, as attackers can remain undetected while exploring the victim’s environment for further exploitable data.
Who Is Most at Risk
Industries that regularly utilize AI tools in their operations—such as marketing, finance, and tech—are particularly vulnerable to these phishing attacks. Organizations of various sizes, especially small to medium enterprises lacking robust cybersecurity frameworks, may unwittingly expose themselves to risks associated with compromised employee credentials or sensitive customer data. As marketing methods increasingly integrate AI capabilities, the potential for destruction grows, especially with personal data or trade secrets at stake.
Defensive Actions and Recommendations
In light of this emerging threat, organizations must take immediate and strategic steps to fortify defenses. Immediate actions should include:
Increased Awareness Training: Conduct targeted training sessions focusing on phishing tactics and the specific risks associated with AI tools. Resources from the NIST Cybersecurity Framework should be leveraged to create robust training materials.
Email Filtering and Reporting Mechanisms: Enhance email gateways to identify and filter suspicious communications effectively. Implement robust reporting systems allowing employees to flag potential phishing attempts.
- Validate External Communications: Adopt strict protocols for verifying the authenticity of communication that involves sensitive actions, establishing a multi-factor verification system for changes in account details or sensitive transactions.
For long-term strategies, organizations should:
Regularly Update Software: Ensure that all software, especially AI tools integrated into operations, is continuously updated to protect against exploited vulnerabilities.
Implement Phishing Simulation Programs: Constantly test employees with simulated phishing attacks to keep awareness high and improve incident response times.
- Utilize Security Services: Consider partnering with cybersecurity firms to gain insights into the evolving landscape of phishing threats, leveraging threat intelligence services for proactive vulnerability assessments.
Regulatory and Legal Exposure
Organizations must also be cognizant of their regulatory environment regarding data breaches. Depending on the nature of the compromised data, industries covered by regulations like the General Data Protection Regulation (GDPR), Health Insurance Portability and Accountability Act (HIPAA), or California Consumer Privacy Act (CCPA) may face strict reporting obligations. Immediate disclosure to affected parties could be mandated alongside potential fines for non-compliance. Not addressing breaches adequately can lead to reputational damage and erosion of consumer trust, compounding legal ramifications.
Full Circle Cyber Analyst Takeaway
The rise of intelligent phishing platforms based on AI technologies demonstrates that attackers are not just expanding their tools but also innovating their approaches to exploit technology’s increasing role in business operations. Organizations must elevate their vigilance, understanding that protecting against such nuanced threats is now an integral part of their cybersecurity strategy. Security teams should function as dynamic entities—capable of adjusting protocols and educating employees regularly to counter these increasingly sophisticated phishing attempts.

